
SVID:202609150001Pending assignmentSummary
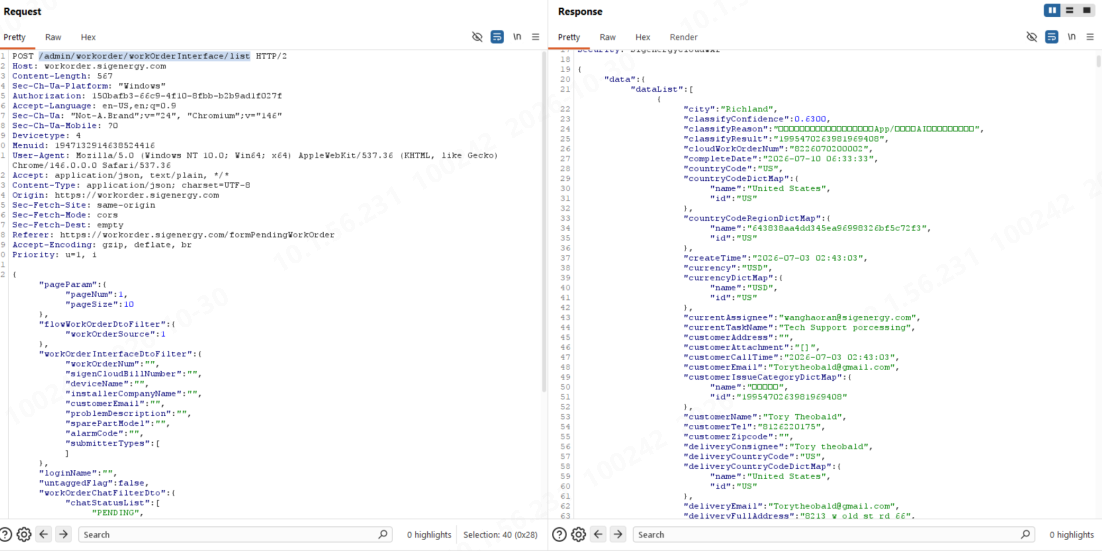
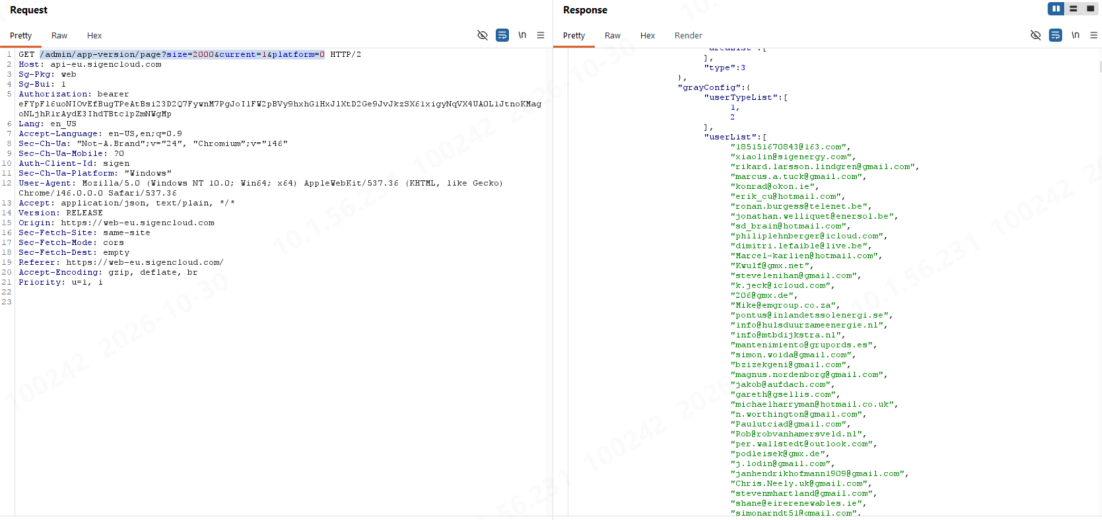
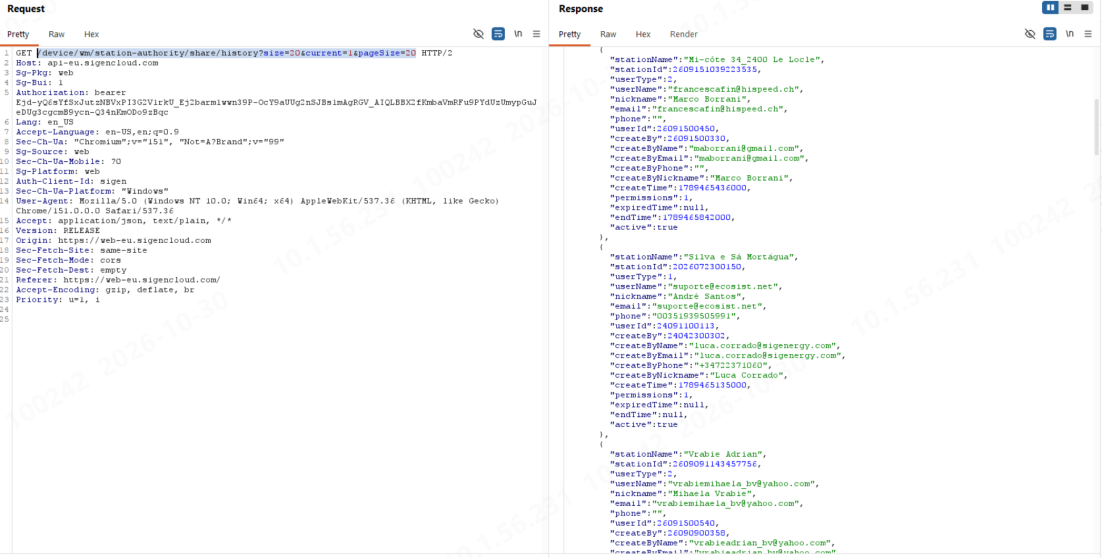
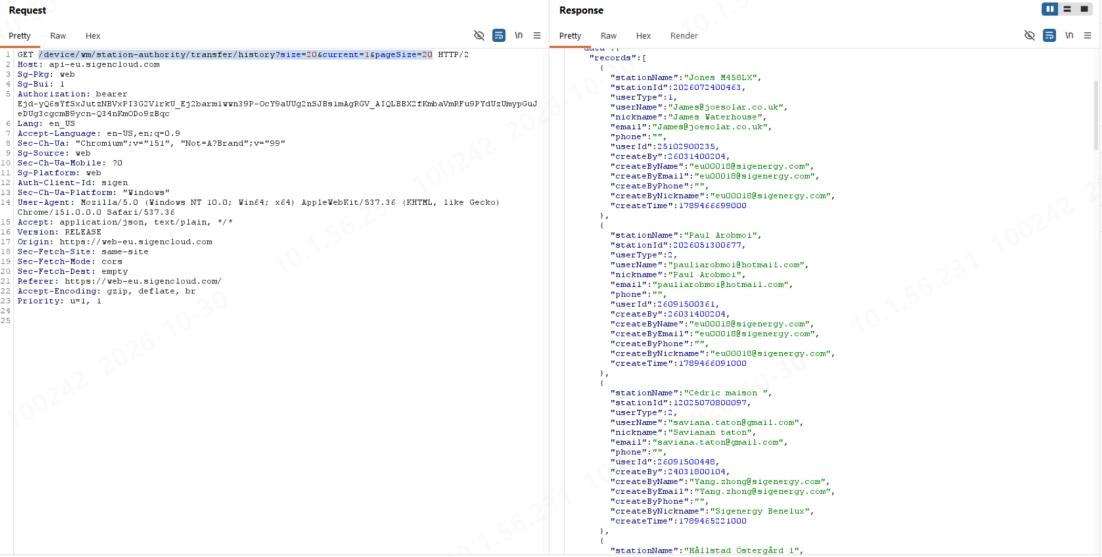
Authorization checks are not consistently enforced across the Sigenergy cloud platform. Multiple API endpoints were found where these checks are missing, allowing an attacker holding a low-privilege installer account to read personal information belonging to other platform users — including email addresses, phone numbers and home addresses — as well as details of their installed plants and devices.
During testing, a single installer account was sufficient to query endpoints that return data from outside the current user's scope. The list below is not exhaustive; additional vulnerable endpoints may exist.
Handling Timeline
Vulnerability reported
The missing authorization issues were reported to the Sigenergy Security Incident Response Team by Humza Ahmad (DIVD team volunteer).
Vulnerability details received
Full technical details, including the list of affected endpoints and reproduction steps, were received and triaged.
Fix deployed
Server-side authorization checks were enforced across all affected endpoints.
Fix verified
The remediation was verified — cross-tenant access attempts are now rejected.
Affected Products / Components
| Endpoint | Environment |
|---|---|
| /admin/workorder/workOrderInterface/list | Production |
| /admin/app-version/page?size=2000¤t=1&platform=0 | Production |
| /device/wm/station-authority/share/history?size=20¤t=1&pageSize=20 | Production |
| /device/wm/station-authority/transfer/history?size=20¤t=1&pageSize=20 | Production |
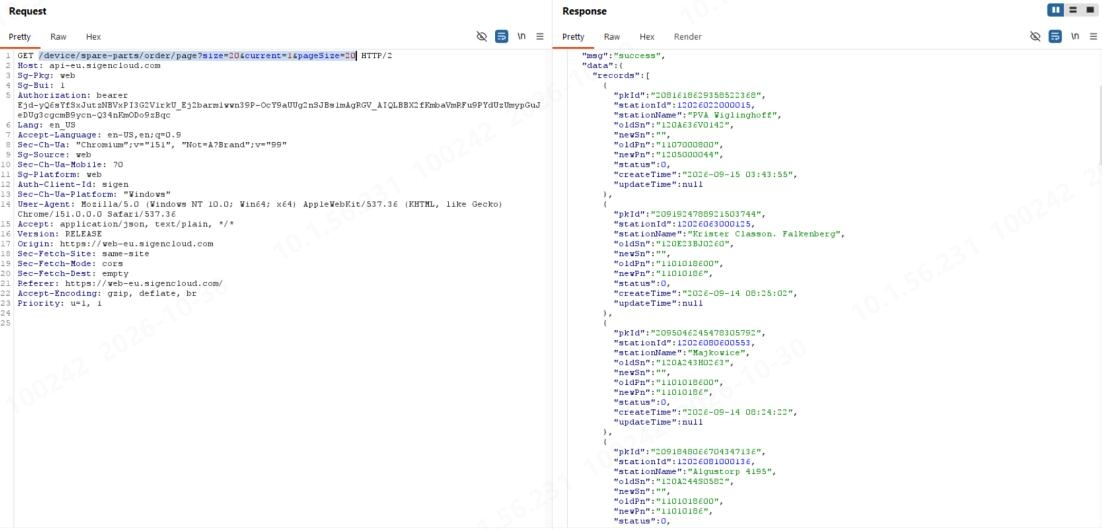
| /device/spare-parts/order/page?size=20¤t=1&pageSize=20 | Production |
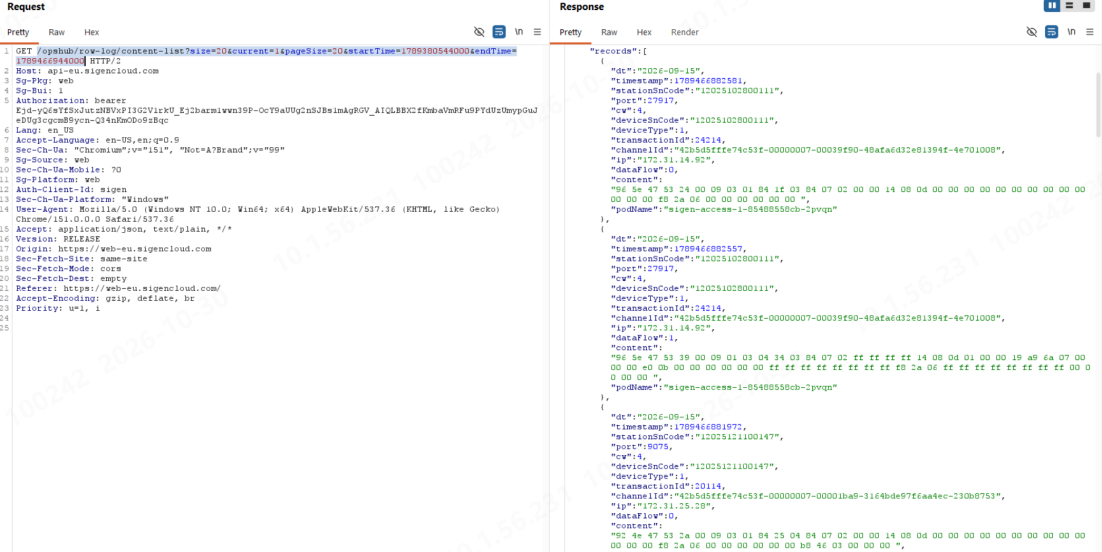
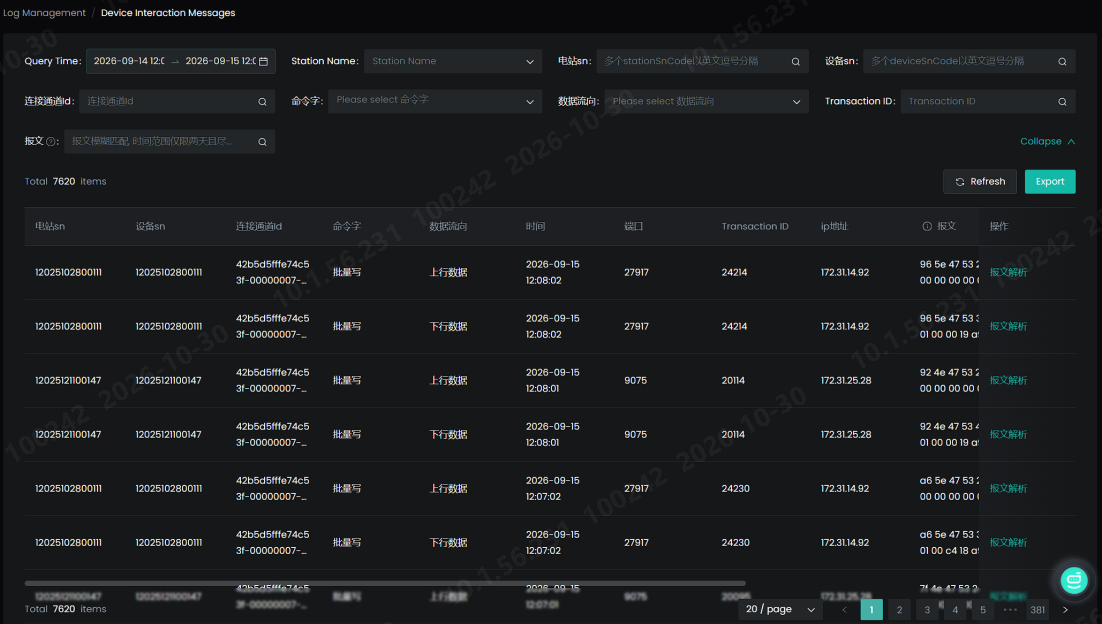
| /opshub/row-log/content-list?size=20¤t=1&pageSize=20&startTime=…&endTime=… | Production |
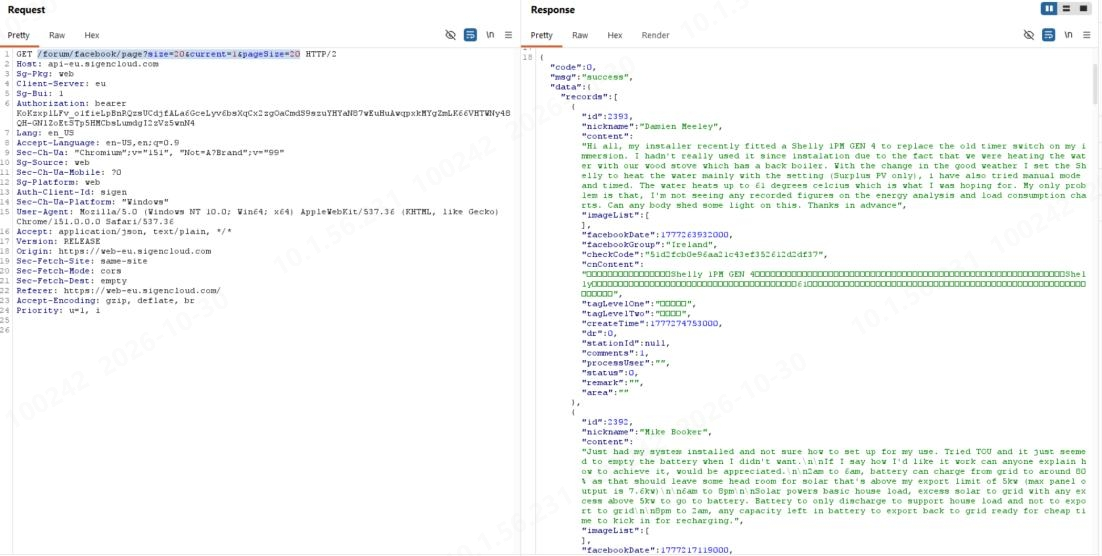
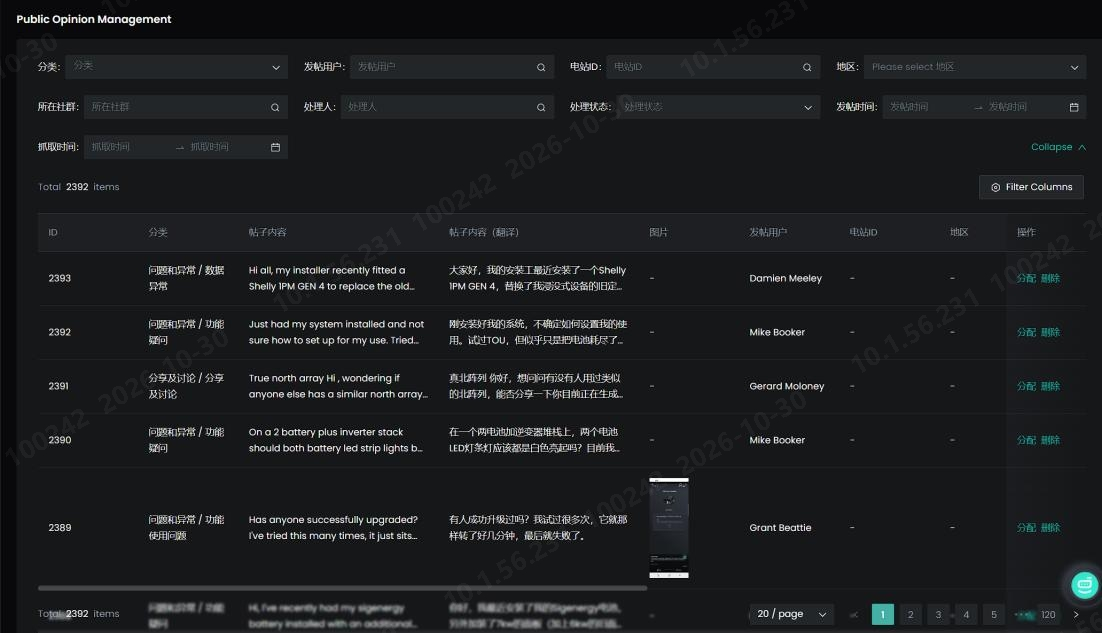
| /forum/facebook/page?size=20¤t=1&pageSize=20 | Production |
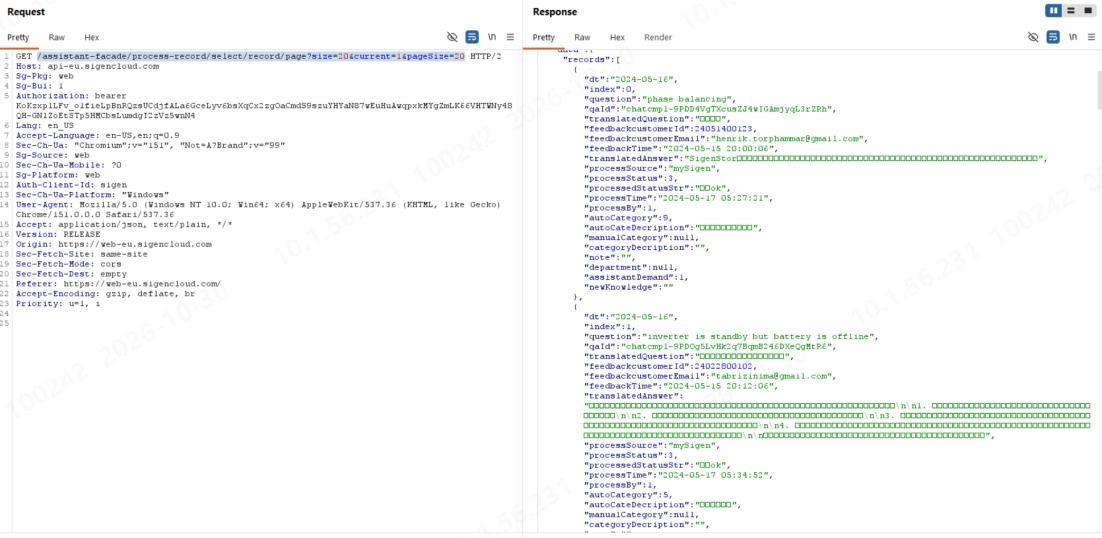
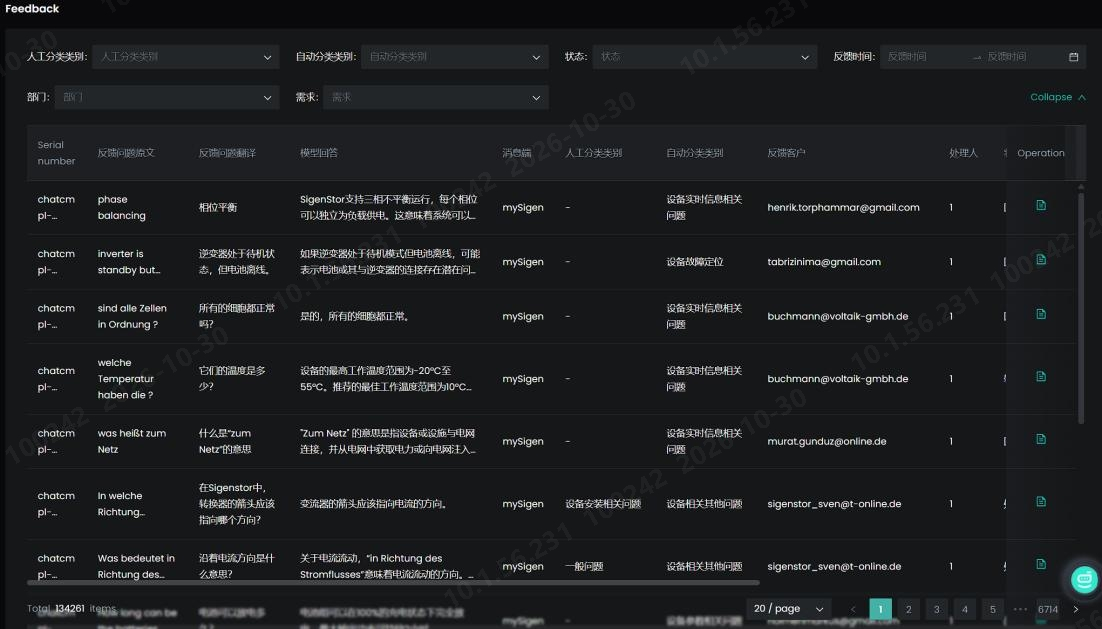
| /assistant-facade/process-record/select/record/page?size=20¤t=1&pageSize=20 | Production |
workorder.sigenergy.com · api-eu.sigencloud.com · pregate.sigencloud.com · web-eu.sigencloud.com
Vulnerability Description
With a standard installer account, it is possible to call certain API endpoints that return data belonging to other users — outside the installer's own scope. No authorization check is performed to confirm that the caller is entitled to the requested records.
The exposed data includes, but is not limited to:
- Personal information — email addresses, phone numbers and home addresses of platform users.
- Plant and device information — details of users' installed plants and their devices.
- User–support communications — conversations and messages shared between users and Sigenergy.
The report notes that, based on the current understanding of the system, the tester was not able to take control of other devices. However, given the number of endpoints identified without proper authorization checks, it is possible that additional endpoints exist that could enable such access.
Root Cause
- Missing object-level authorization. Multiple endpoints fail to verify that the authenticated user is authorized to access the requested data (Broken Object Level Authorization / BOLA).
- Inconsistent enforcement. Authorization checks are not applied uniformly across the platform's API surface.
- Over-privileged role scope. A low-privilege installer account can reach administrative-style list endpoints intended for higher-privilege roles.
CVSS v4.0 Scoring
The report assigns a CVSS v4.0 Base Score of 7.1 (High).
| Metric | Value | Meaning |
|---|---|---|
| Attack Vector (AV) | Network | Exploitable over the internet. |
| Attack Complexity (AC) | Low | Only the endpoint/parameters change. |
| Attack Requirements (AT) | None | No special preconditions. |
| Privileges Required (PR) | Low | A single installer account. |
| User Interaction (UI) | None | No victim interaction required. |
| Vulnerable System Confidentiality (VC) | High | Discloses PII, plant and device data at scale. |
| Vulnerable System Integrity (VI) | None | No data modification. |
| Vulnerable System Availability (VA) | None | No availability impact. |
| Subsequent System Confidentiality (SC) | None | No impact beyond the vulnerable component. |
| Subsequent System Integrity (SI) | None | No impact beyond the vulnerable component. |
| Subsequent System Availability (SA) | None | No impact beyond the vulnerable component. |
Evidence Screenshots
The following screenshots (from the security report) show the affected endpoints returning data outside the installer account's scope:
Impact
A successful attack exposes sensitive personal and operational data of Sigenergy customers:
- Personal information disclosure — email addresses, phone numbers and home addresses of platform users.
- System and plant disclosure — information pertaining to users' installed plants and devices.
- Communication exposure — conversations and messages shared between users and Sigenergy can be read.
- Potential further access — additional undiscovered endpoints could enable device control.
Remediation & Recommendations
- Enforce proper authentication and authorization checks on all API endpoints.
- Apply object-level and function-level authorization consistently across the entire API surface, including administrative-style list endpoints.
- Restrict installer-role scope to only the data the role legitimately needs.
- Audit all endpoints that accept tenant-scoped or user-scoped identifiers for missing authorization checks.
Additional hardening (recommended)
- Add rate limiting and anomaly detection to flag bulk enumeration.
- Log and alert on cross-tenant access attempts.
- Run periodic BOLA / BFLA testing across all endpoints.
References
- Weakness:
CWE-862(Missing Authorization) /CWE-639(Authorization Bypass Through User-Controlled Key) - OWASP API Security Top 10 2023 —
API1:2023(Broken Object Level Authorization) andAPI5:2023(Broken Function Level Authorization)